Disclosure wording, timing, and internal controls determine whether a public company faces meaningful securities litigation risk under Rule 10b-5 and related doctrines. The two highest-leverage failure points are risk-factor language that has gone stale relative to known internal facts and a disclosure-control process that cannot document how a materiality call was made. Fixing escalation pathways, refreshing company-specific cautionary language, and building an audit trail (the kind of forensic record a forensic analytics methodology can surface) reduce exposure more reliably than any single legal argument raised after a complaint is filed.
TL;DR:
- Companies with unchanged risk-factor language across multiple filings and no documented materiality assessments face increased litigation risk from stale or overstated disclosures.
- Internal escalation delays, especially when internal teams flag issues weeks before public disclosure, significantly heighten the chance of securities claims.
- Legal protections for forward-looking statements diminish if disclosures lack company-specific caution or contradict internal knowledge, increasing liability exposure.
- Regular forensic audits comparing internal findings with public record can identify disclosure gaps and reduce vulnerability to hypothetical risk-factor claims.
- Building documented, cross-functional disclosure processes before issues arise creates a strong defense and mitigates the size and scope of potential securities lawsuits.
Table of Contents
- How Common Is Litigation Risk From Disclosures?
- What Legal Standards Govern Disclosure Liability?
- How Does the Hypothetical Risk-Factor Doctrine Work?
- When Does Timing Create the Most Litigation Exposure?
- How Does Litigation Risk Shape Disclosure Behavior?
- What Defense Strategies Reduce Disclosure Litigation Exposure?
- How Should Teams Audit Disclosures for Red Flags?
- Forensic Perspective: How Lacunaindex Analyzes Disclosure Gaps
- What Counsel and CFOs Should Prioritize Now
- Lower Disclosure-Driven Litigation Risk With Lacunaindex
- Primary Sources and Datasets to Consult
- Sources
- FAQ
How Common Is Litigation Risk From Disclosures?
Disclosure-linked litigation is not a rare tail event for large public issuers. It is a recurring feature of the corporate life cycle, concentrated in predictable industries and triggered by predictable events: earnings misses, restatements, cyber incidents, and regulatory actions that contradict a company's prior public statements.
Empirical research from Billings and coauthors, published in the Journal of Accounting Research, uses structured federal court data to measure how litigation incidence correlates with disclosure practices and firm characteristics. The study's core finding is that firms are not randomly sued. Litigation incidence tracks specific, observable traits: prior disclosure volume, industry volatility, and the size and direction of stock-price moves around a corrective event. Firms with a pattern of aggressive forward-looking claims and thin cautionary language show up disproportionately in the litigation data relative to more conservative disclosers.
Researchers and practitioners rely on a small set of tools to build these datasets and to track individual matters in real time:
- PACER (Public Access to Court Electronic Records) provides the underlying federal docket access that lets analysts pull complaints, motions, and rulings directly from the source rather than from secondhand summaries.
- The Federal Judicial Center (FJC) maintains structured case metadata, including the Integrated Database, which researchers use to classify case types and outcomes at scale.
- The Stanford Securities Class Action Clearinghouse and comparable identifiers help separate securities class actions from adjacent categories of disclosure-related exposure.
That last distinction matters for anyone scoping litigation risk. A securities class action under Rule 10b-5 is only one branch of disclosure liability. Alongside it sit SEC enforcement actions and administrative proceedings, shareholder derivative suits alleging board-level oversight failures, and state or federal regulatory investigations that never reach a courtroom but still generate discovery costs, reputational damage, and settlement exposure. A company can face meaningful financial and governance consequences of a disclosure dispute even when no class action is ever certified.
What Legal Standards Govern Disclosure Liability?
The statutory backbone of disclosure litigation is Rule 10b-5, and understanding its mechanics is the difference between a defensible disclosure and an actionable one.
Rule 10b-5(b) makes it unlawful to make an untrue statement of a material fact, or to omit a material fact necessary to make an existing statement not misleading, in connection with the purchase or sale of a security. The omissions half of that standard is where most modern disclosure litigation actually lives. A statement does not need to be false on its face to trigger liability; it becomes actionable when the company knew something that made an existing, technically true statement misleading by omission. This is the mechanism that converts stale risk-factor boilerplate into a securities fraud claim: continuing to say a data breach "could" happen after one has already occurred is not a hypothetical anymore.
Two doctrines exist specifically to protect forward-looking statements from this exposure, and practitioners frequently misjudge their scope.
- The PSLRA forward-looking statement safe harbor, enacted as part of the Private Securities Litigation Reform Act, protects projections and forward-looking claims when they are identified as such and accompanied by meaningful cautionary language.
- The bespeaks-caution doctrine, a related judicial construct, holds that sufficiently specific warnings accompanying a forward-looking statement can render an alleged misrepresentation immaterial as a matter of law.
Both protections collapse under the same condition: courts require cautionary language that is company-specific and meaningful, not generic or boilerplate. A risk factor that could be copied and pasted into any competitor's 10-K, and that says nothing about what the company actually knows about its own exposure, typically fails to earn safe-harbor protection once litigation begins. Courts have also grown more skeptical of safe-harbor defenses when internal documents show the company had actual knowledge contradicting its public caution at the time the statement was made.
Pleading standards add another layer of complexity. A private Rule 10b-5 claim requires plaintiffs to plead scienter, meaning the defendant acted with intent to deceive or severe recklessness, a standard the PSLRA heightened specifically to deter weak securities suits. SEC enforcement actions, by contrast, can proceed on negligence-based theories under related provisions, which is one reason regulatory risk and private litigation risk do not always move in tandem. Materiality, meanwhile, remains the threshold question in every disclosure case: information is material if a reasonable investor would consider it important to an investment decision, and remedies for a successful 10b-5 claim typically include compensatory damages tied to the stock-price decline attributable to the corrective disclosure.
How Does the Hypothetical Risk-Factor Doctrine Work?
The single doctrinal development that reshaped disclosure litigation over the past decade is the hypothetical risk-factor theory, and its origin point is Mylan.
The Mylan litigation established the pattern that has since repeated across industries: a company frames a known or ongoing issue in "we may face" or "could result in" language in its risk factors, even after the underlying event has already begun to materialize internally. Plaintiffs argue that this framing is itself the misrepresentation. Courts have found this theory persuasive when internal records show the company was tracking the issue as a live concern while its public disclosures described it as speculative.
The theory has since traveled well beyond its origin. In the In re Alphabet litigation, plaintiffs argued Google's risk-factor language around a known product vulnerability had gone stale relative to what engineering and legal teams already knew internally. The SolarWinds matter produced a landmark SEC enforcement action alleging the company's cybersecurity risk disclosures described generic, hypothetical risks while the company's own security personnel had flagged specific, known vulnerabilities. Peloton faced Second Circuit scrutiny over whether statements about subscriber growth and demand crossed from optimistic projection into misleading assurance once internal sales data pointed the other way. First American drew SEC attention over data-security disclosure controls following a breach that exposed how internal escalation had failed to reach the disclosure committee in time. Chegg faced similar scrutiny after its risk disclosures around competitive pressure from generative AI tools were tested against what leadership already knew about enrollment trends.
Across these matters, courts and enforcement staff apply a consistent factual test. A "could happen" statement is treated as describing a present condition, not a hypothetical, when the record shows most of the following:
- Internal teams, IT/security functions, or product groups had already flagged the issue as active, not speculative.
- Risk-factor language remained unchanged across multiple filing periods despite the internal escalation.
- The disclosure incorporated older risk language by reference rather than updating it to reflect new facts.
- No documented materiality assessment exists showing the company actually considered whether the risk had crystallized.
- Public statements in earnings calls or press releases affirmatively contradicted the internal record.
Pro Tip: If your risk-factor section has not changed in substance across three or more consecutive filing periods while the underlying business has changed materially, that static language is itself a red flag plaintiffs' counsel will flag first.
Enforcement outcomes in this space span a wide range depending on scope and cooperation. SEC administrative orders for disclosure-control and cybersecurity-disclosure failures have ranged from moderate civil penalties for narrower, self-reported gaps to substantially larger sanctions where the agency found sustained, uncorrected internal-control breakdowns. The common denominator across these enforcement examples is not the size of the underlying event but the size of the gap between what the company knew internally and what it told the market.
When Does Timing Create the Most Litigation Exposure?
The interval between internal discovery of a material fact and its public disclosure is the single highest-risk window in the entire disclosure life cycle, and it is where most successful claims find their strongest factual support.
The SEC's disclosure rules effective in December 2023 sharpened this exposure rather than eliminating it. The rules generally require issuers to disclose a material cybersecurity incident within four business days of determining materiality, via Form 8-K. That structure sounds precise, but the rule's real pressure point is the materiality determination itself, which happens before the clock starts. A company that delays concluding an incident is material, even while internally treating it as significant, opens a gap that plaintiffs and the SEC can both use as evidence of an artificially manufactured buffer.
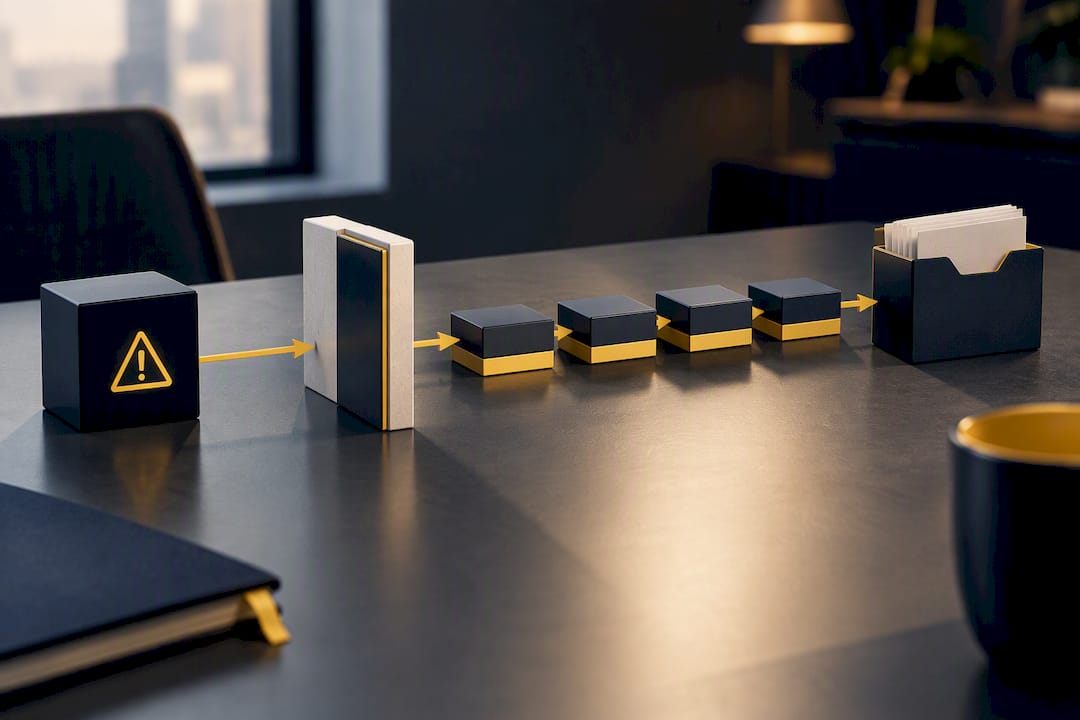
Inconsistent narratives across filing types compound this exposure. A risk-factor section describing an issue as speculative, sitting alongside an 8-K or 10-Q that treats the same issue as already resolved or contained, hands plaintiffs a ready-made contradiction to plead. Escalation failures, meaning the internal chain by which a discovered issue is supposed to reach the disclosure committee or general counsel, are among the most commonly cited factual bases in enforcement orders and complaints. When that chain breaks down, or when no one can produce a record showing when the materiality question was actually raised, the absence of documentation becomes evidence against the company by default.
Consider a straightforward pattern: a company's security team identifies unauthorized access to customer data on a Tuesday. Legal is not looped in until the following week, and no formal materiality memo is drafted until the 8-K is filed three weeks later. In litigation, plaintiffs will not need to prove the company acted with malice. They will simply point to the internal timeline, the absence of a contemporaneous materiality analysis, and the delay itself as circumstantial evidence that the company knew the issue was significant and slow-walked its disclosure.
- Document the exact date internal teams first identified the issue.
- Record who made the materiality call and the reasoning behind it, not just the conclusion.
- Track every version of related risk-factor language across filing periods for consistency.
- Preserve cross-functional communications between security, product, finance, and legal teams.
How Does Litigation Risk Shape Disclosure Behavior?
Litigation risk does not simply punish bad disclosures after the fact. It actively shapes what companies choose to say and when, sometimes in counterintuitive directions.
Academic economic modeling of this dynamic identifies a genuine tension between deterrence and insurance effects. Higher litigation risk generally deters firms from withholding severely negative news, because the downside of getting caught outweighs the short-term benefit of silence. But the same research shows that elevated litigation risk can also push firms toward withholding moderately negative information, because the act of disclosing itself becomes the trigger for a lawsuit. In other words, litigation risk is not a uniform disincentive toward silence. It can suppress disclosure of exactly the ambiguous, middle-tier bad news that later turns out to matter most to investors.
The market mechanics behind most securities class actions follow a consistent sequence. A company issues an optimistic or reassuring disclosure. Internal conditions diverge from that narrative. A corrective disclosure eventually surfaces, whether through a restatement, a missed earnings guidance number, a regulatory action, or a leaked internal document, and the stock price drops sharply on the news. That price decline is the evidentiary anchor for loss causation in the ensuing class action, and plaintiffs' experts will typically isolate the portion of the drop attributable specifically to the corrective information.
Certain sectors show up disproportionately in this pattern:
- Technology and cybersecurity firms face concentrated exposure because breach timelines create sharp, documentable gaps between internal knowledge and public disclosure.
- Life sciences and pharmaceutical companies face frequent litigation tied to clinical trial results and regulatory approval disclosures, where binary outcomes create large, discrete price moves.
- High-growth companies with aggressive forward guidance face elevated risk when internal metrics diverge from the growth narrative told to investors, a pattern visible in the Peloton litigation.
What Defense Strategies Reduce Disclosure Litigation Exposure?
The strongest defense against disclosure litigation is built months or years before any complaint is filed, not in response to one.
Process-based disclosure defenses have become one of the most consequential developments in this area. The theory is straightforward: if a company can show a documented, systematic, cross-functional review process for evaluating materiality and drafting disclosures, that record becomes powerful evidence of good faith, directly undercutting a scienter allegation. Legal analysis of this trend notes that firms can rely on disclosure processes as evidence of good faith without necessarily waiving privilege over the underlying legal advice, because the process itself, not the substance of counsel's recommendations, is what gets documented and produced.
Building that record and avoiding the drafting mistakes that undermine it requires a few concrete practices:
- Maintain a disclosure committee log capturing the date and content of internal discovery for any potentially material issue.
- Record cross-functional notices between IT/security, product, finance, and legal, showing the information actually reached decision-makers.
- Document who made each materiality call, the specific rationale, and what alternative was considered and rejected.
- Capture contemporaneous remediation decisions so the timeline shows action, not just awareness.
- Replace boilerplate risk-factor language with company-specific cautionary statements tied to the company's actual known exposures, refreshed every filing cycle rather than carried forward by habit.
Courts increasingly treat this kind of documented protocol as meaningful evidence, particularly when a company can show the same rigor applied consistently across multiple disclosure cycles rather than being assembled retroactively after litigation began.
Pro Tip: Draft your materiality memo the same week the underlying issue surfaces, not the week before the 8-K is due. A memo written under litigation pressure reads very differently to a judge than one written in the ordinary course of business.
Internal-control quality tied to Sarbanes-Oxley's ICFR requirements plays a supporting role here too. Weak internal control over financial reporting does not just create audit findings; it removes the evidentiary foundation a company needs to argue its disclosure process was reliable, which matters at the motion-to-dismiss stage where courts assess whether the complaint plausibly alleges scienter.
How Should Teams Audit Disclosures for Red Flags?
A disciplined audit of existing filings, run before litigation ever surfaces, is the most cost-effective risk-reduction step available to legal and finance teams.
- Compare risk-factor language across multiple recent filing periods and flag any section that has remained substantively unchanged despite known business developments.
- Cross-check risk factors against 8-K and 10-Q narratives for the same underlying issue, looking for tense shifts from hypothetical to past-tense that were never reflected back in the risk factors.
- Review earnings-call transcripts for optimistic characterizations that contradict internal metrics discussed in board materials.
- Pull timestamps on internal escalation records and compare them to the filing date of the related disclosure.
- Identify third-party signals, analyst downgrades, regulatory inquiries, whistleblower reports, that preceded a disclosure and check whether they were addressed internally before going public.
Collecting the right documentary evidence matters as much as running the checklist itself. Materiality memos, escalation emails, disclosure-committee minutes, and version histories of risk-factor drafts are the specific evidence that rebuts scienter allegations, because they show a reasoned, documented process rather than silence followed by a lawsuit. A forensic taxonomy of common omission types can help teams categorize findings consistently across business units.
| Risk signal | What it indicates | Priority |
|---|---|---|
| Unchanged risk-factor language across 4+ periods | Stale hypothetical framing, hypothetical-doctrine exposure | High |
| No materiality memo on file for a known issue | Missing process-defense evidence | High |
| Escalation gap over 2 weeks | Documentable timing exposure under SEC rules | High |
| Earnings-call optimism vs. internal metrics | Potential 10b-5(b) misstatement exposure | Medium |
| Generic, boilerplate cautionary language | Weak PSLRA safe-harbor protection | Medium |
Triaging findings this way lets audit committees build a remediation roadmap ranked by actual litigation exposure rather than by whichever issue surfaced most recently. High-priority findings, particularly missing materiality documentation, deserve immediate remediation because they cannot be fixed retroactively once a dispute arises.
Forensic Perspective: How Lacunaindex Analyzes Disclosure Gaps
Lacunaindex approaches disclosure risk from a different angle than traditional legal review: it measures the gap between what a company says and what its own public record shows it actually delivered, using narrative-forensics methodology applied to filings, earnings calls, press releases, and proxy statements.
Delivery versus narrative can be quantified through execution scores, and companies can be classified into archetypes based on the pattern that emerges. A company classified as having borrowed narrative typically shows a history of forward-looking claims that outpace demonstrated execution. That pattern is exactly the kind of factual record plaintiffs' counsel look for when building a hypothetical risk-factor claim, since a company whose narrative has consistently run ahead of its results is more likely to have described a known internal shortfall in speculative, forward-looking language rather than acknowledging it directly.
This matters for litigation-risk assessment because the correlation between quantified narrative gaps and subsequent corrective events means these gaps are not just a reputational or valuation concern. They are a leading indicator of where disclosure liability is most likely to materialize next.
- Execution scores flag companies where public claims have historically diverged from documented results.
- Archetype classification (earned, borrowed, undervalued) helps prioritize which filings merit deeper legal or forensic review.
- Sector benchmarks let governance and legal teams see whether a company's narrative gap is unusual for its industry or consistent with peers.
Legal and finance teams using this kind of output alongside their own internal audit process, rather than as a replacement for it, gain an evidence-based way to prioritize which business units or disclosure sections deserve the closest scrutiny before the next filing cycle.
What Counsel and CFOs Should Prioritize Now
The conventional advice to "review your risk factors annually" understates the problem. Annual review misses the interim period where internal facts diverge from public language, which is exactly where the hypothetical risk-factor doctrine does its damage. The near-term priority is fixing escalation pathways so a discovered issue reaches the disclosure committee within days, not weeks, and documenting every materiality call in real time rather than reconstructing the rationale after a complaint arrives.
At the board and audit-committee level, disclosure-control testing deserves the same recurring rigor as financial-control testing under ICFR, not a lighter-touch annual checkbox. Heading into 2026, expect litigation theories to sharpen around AI capability claims, ESG progress metrics that outpace verified results, and cybersecurity incident timelines tested against the SEC's four-day disclosure trigger. Each of these follows the same underlying pattern that this article has traced from Mylan forward: a gap between internal knowledge and public narrative, left undocumented.
— Glen
Lower Disclosure-Driven Litigation Risk With Lacunaindex
The alternative to waiting for a plaintiffs' firm to find your narrative gaps first is finding them yourself, using the same public records they will use against you. Lacunaindex's forensic analytics quantify the distance between what a company claims in filings, earnings calls, and press releases and what its own disclosed results actually show, giving legal and finance teams an evidence-based way to prioritize which risk factors and disclosure sections need attention before the next filing cycle, not after a demand letter arrives.
Per-company analysis delivers a forensic report on a specific issuer, scoring execution against narrative and flagging the kind of stale or overstated language that fuels hypothetical risk-factor claims. The Cohort Pulse and Sector Sweep plans extend that view across peer groups, letting audit committees and governance teams benchmark a company's disclosure patterns against its sector rather than reviewing filings in isolation. Each score traces back to a specific public document, which matters when the underlying question is whether a disclosure record would hold up under the same scrutiny plaintiffs' counsel applies. Review pricing and plan details or pull up a sector benchmark for your industry to see where the gaps typically show up.
Primary Sources and Datasets to Consult
Practitioners verifying claims in this article, or building their own incidence analysis, should start with these primary resources:
- Rule 10b-5, via Cornell Law School's Legal Information Institute, for the statutory text and doctrinal summary.
- SEC disclosure rules and press releases, including the 2023 cybersecurity disclosure rule announcement, for current timing requirements.
- PACER, at Pacer, for direct access to federal court dockets and filed complaints.
- The FJC's Integrated Database, for structured, research-grade case metadata across federal courts.
- Billings et al.'s incidence study in the Journal of Accounting Research, available via DOI, for empirical findings on litigation frequency and firm characteristics.
This article is general information, not a substitute for advice from a qualified financial advisor. Consult a qualified financial professional about your own circumstances before acting on anything here.
Sources
- Incidence, Risk, and Disclosure of Corporate Litigation — Billings et al. (Journal of Accounting Research)
- Rule 10b-5 — Cornell Law School LII
- SEC press release on disclosure rules (2023)
FAQ
What Triggers Litigation Risk From Disclosures?
Litigation risk from disclosures typically arises when a company's public statements, including risk factors, diverge from what it knew internally at the time. The most common trigger is omission liability under Rule 10b-5, where a hypothetical warning continues after the underlying event has already occurred.
How Does the Hypothetical Risk-Factor Doctrine Apply to Cybersecurity?
Courts treat continued "may occur" language about a cyber incident as potentially misleading once internal security teams have confirmed the incident is active. This pattern appeared in the SEC's enforcement action against SolarWinds and in related enforcement examples involving stale risk-factor language.
Does the PSLRA Safe Harbor Always Protect Forward-Looking Statements?
No. The safe harbor and the related bespeaks-caution doctrine only protect forward-looking statements accompanied by meaningful, company-specific cautionary language. Generic, boilerplate warnings, or statements made while the company had actual contrary knowledge, typically lose that protection.
What Documentation Best Defends Against a Disclosure Lawsuit?
A documented, systematic disclosure-review process, including materiality memos, escalation records, and cross-functional notices, is the strongest evidence of good faith. This process-based defense can rebut scienter allegations without waiving attorney-client privilege.
How Can Lacunaindex Help Assess Disclosure Litigation Risk?
Lacunaindex scores the gap between a company's public narrative and its documented results, flagging patterns that resemble the factual profile behind hypothetical risk-factor claims. Pricing for the Cohort Pulse and Sector Sweep plans is available directly on the site, and per-company forensic reports are accessible through the benchmarks page.